Join us at Spark 2026 - Nozomi Networks' Customer Conference!
Sign Up
The Nozomi Networks platform helps DoD components and DIB contractors safely automate DISA STIG security configuration assessments for OT assets, consolidate proof of compliance and centrally track changes over time.
Security Technical Implementation Guides (STIGs) are security configuration guides developed and maintained by the Defense Information Systems Agency (DISA) for U.S. Department of Defense (DoD) systems. They translate broader cybersecurity requirements into specific, product-level configuration checks for operating systems, applications, network devices and other technologies, helping organizations implement and assess applicable requirements within the DoD Risk Management Framework and NIST SP 800-53 control structure.
STIGs are relevant for DoD components, defense industrial base (DIB) organizations, systems integrators and service providers supporting DoD environments, and other environments that use DoD security baselines.
STIGS apply to systems running Windows, Linux, macOS and other covered technologies. In DoD environments, the challenge is applying and validating detailed configuration requirements consistently across large, distributed and diverse environments.
Manual
Assessments
Security teams must interpret and validate hundreds of technical configuration requirements manually, making assessments slow and hard to scale.
Distributed Environments
Distributed sites, sensitive systems, diverse operating environments and limited access to host-level configuration data make IT-centric approaches impractical.
Fragmented Evidence
Results are spread across scanners, spreadsheets and reports, making it hard to understand which assets failed which checks, why, and what needs to be remediated.
No Centralized Asset Visibility
Without centralized and repeatable assessments, teams struggle to understand configuration posture and identify when systems move out of compliance.
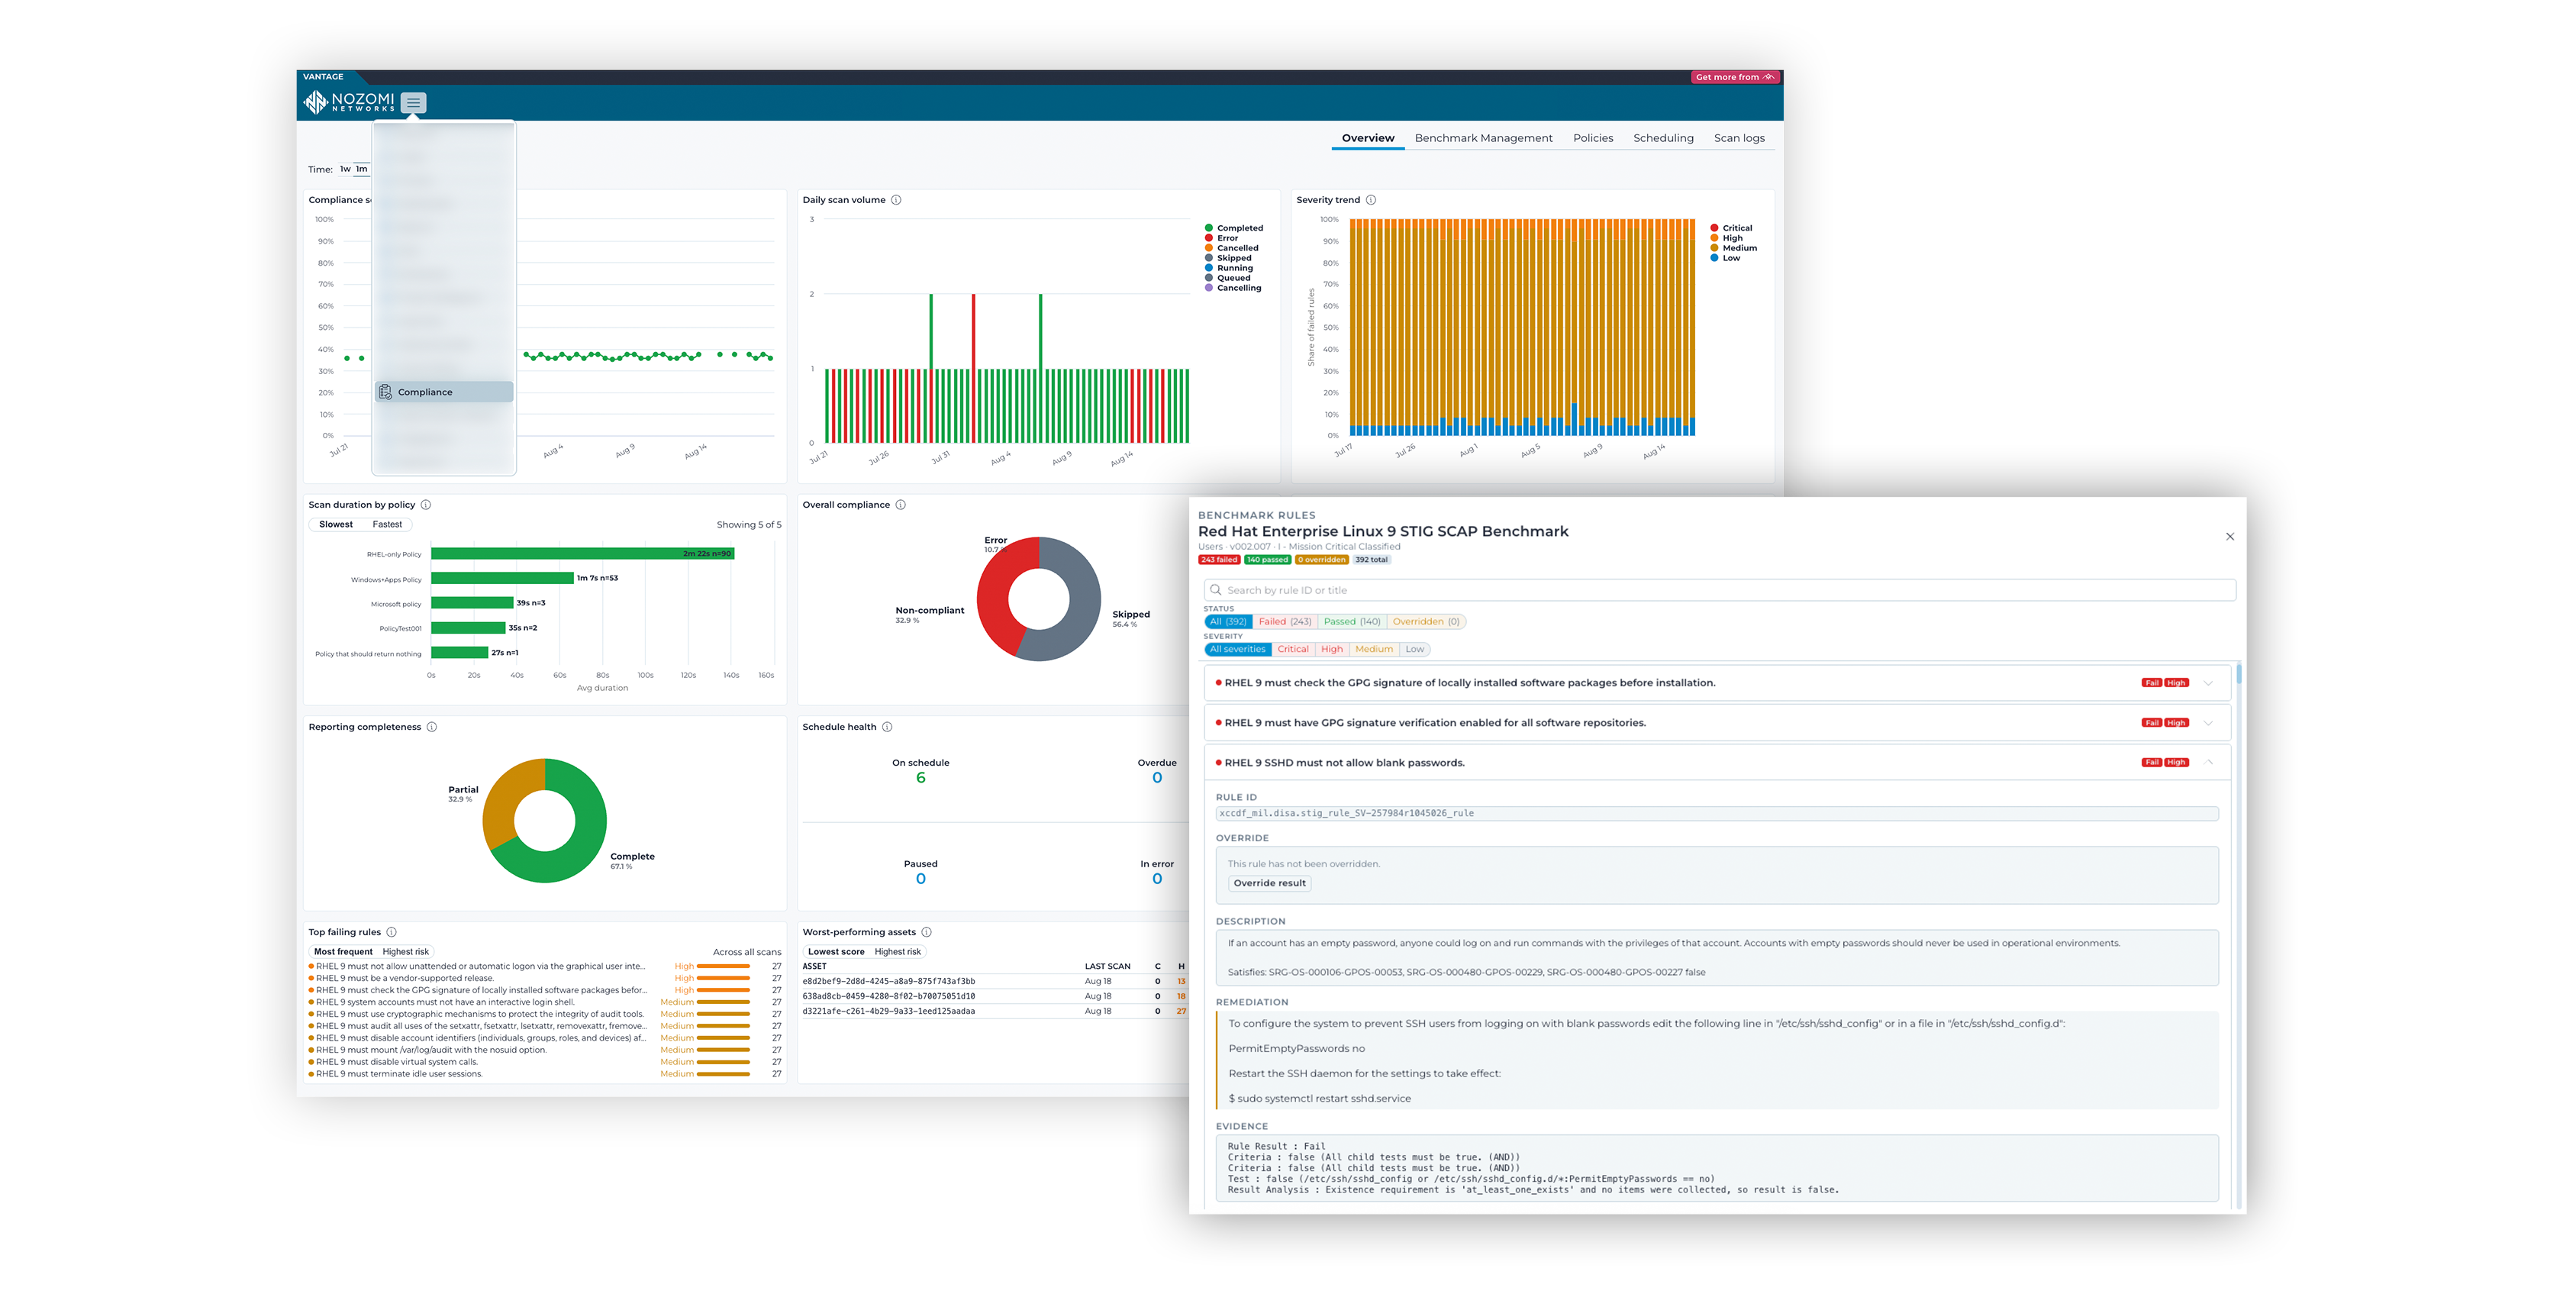
Nozomi Arc sensors automate DISA STIG compliance in distributed OT environments by assessing Windows-, Linux- and macOS-based OT endpoint security configurations against benchmarks, consolidating proof of compliance and centrally tracking changes over time on premises and in Vantage or Vantage for Government, our FedRAMP® Class C (Moderate) SaaS platform.
OT and cyber-physical systems in DoD environments often run on Windows and Linux hosts that are subject to STIG requirements. But distributed sites, operationally sensitive systems and limited access to host-level configuration data make IT-centric assessment approaches impractical.
Nozomi Arc sensors collect configuration evidence directly from OT endpoints, supplemented by passive monitoring of network communications, with safe active polling planned for future releases. Results appear within each asset profile alongside other security information, giving teams consistent, repeatable compliance visibility across OT sites.
The Nozomi Networks Platform provides a safe, scalable way to run repeatable SCAs across distributed environments, centralize results and demonstrate compliance.
Automated
Assessments
Evaluates rules
directly against imported
security benchmarks using endpoint configuration evidence collectedthrough Nozomi Arc sensors and passive network monitoring.
Centralized Visibility & Tracking
Centralizes results across assets, benchmarks, policies and individual checks, with access to rule-level finding to understand what failed and why.

Operationalized for Scale
Runs repeatable, scheduled assessments across distributed environments, with support for centralized on-premises and cloud workflows.

Demonstrated Compliance
Displays pass/fail findings, rule details, collected evidence and remediation guidance across benchmarks and assets, with added context within individual asset profiles.