Join us at Spark 2026 - Nozomi Networks' Customer Conference!
Sign Up
Expanding regulatory requirements, converging cyber risk and AI-enabled automation are changing how critical operations must be secured and managed. Organizations need a real-time OT system of record that understands which assets exist, how they change, who changed them, why decisions were made and whether those decisions remain safe, compliant and effective.

Real-time, accurate asset inventory
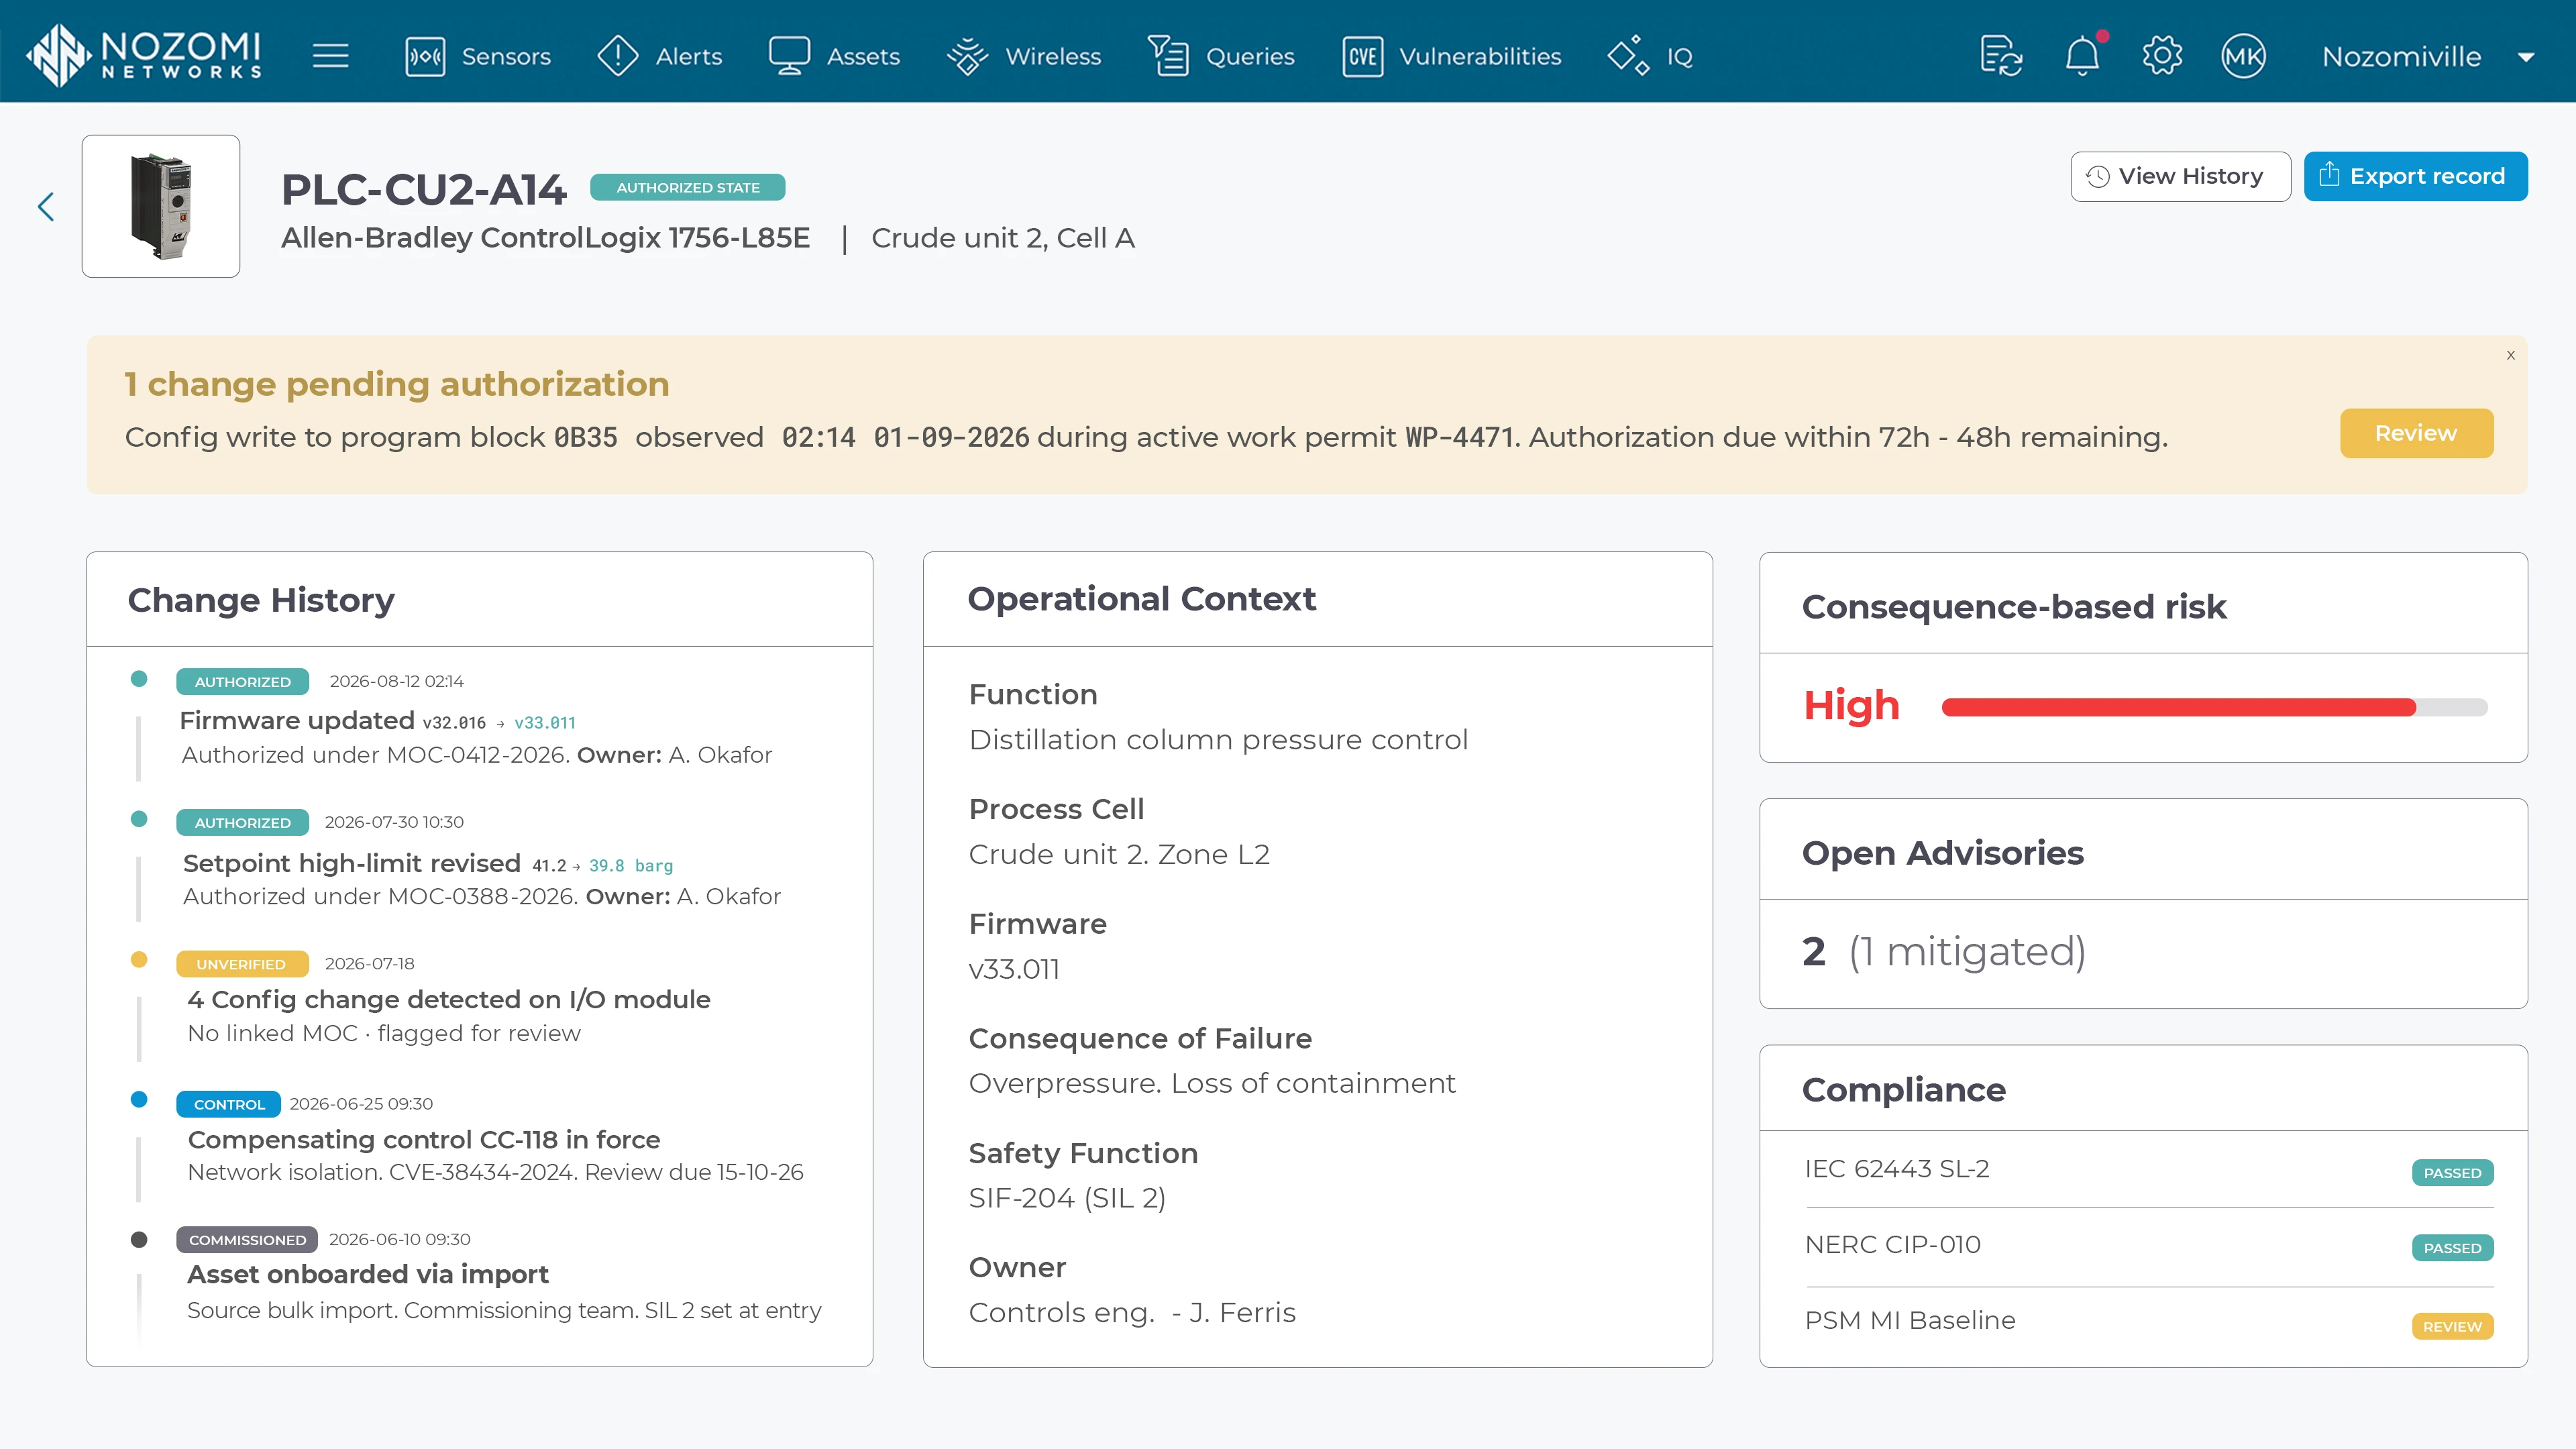
Centralizes asset details across hardware, software, configuration, connectivity and business context, while keeping them accurate in dynamic environments.

Safe change management with tools built for OT
Captures the operational and business context that frontline teams need to make critical decisions, without the pain and cost of modifying off-the-shelf tools designed for IT.

Compliance evidence that keeps pace
Continuously tracks and updates audit evidence as regulatory requirements evolve, avoiding the scramble to assemble evidence at audit time.
Nozomi Compass is the only OT-native asset and service management platform built on the deepest first-party asset data. It delivers defensible compliance, governed change and real risk reduction.
Built on a source of truth. Every workflow, risk score and audit runs on the broadest, most current OT asset record, always a complete and real-time picture.

Maintain one trustworthy record that allows better risk decisions, compliance reporting and change governance.
Enrich asset records with process, safety, hierarchy, dependency and business context.
Preserve a history of what changed, when it changed, why it changed and whether the change was authorized.
Prioritize actions using asset state, operational impact, regulatory requirements and mitigating controls.
Share trusted context across connected tools such as CMDB, IT asset management, IT service management, engineering and other enterprise systems.
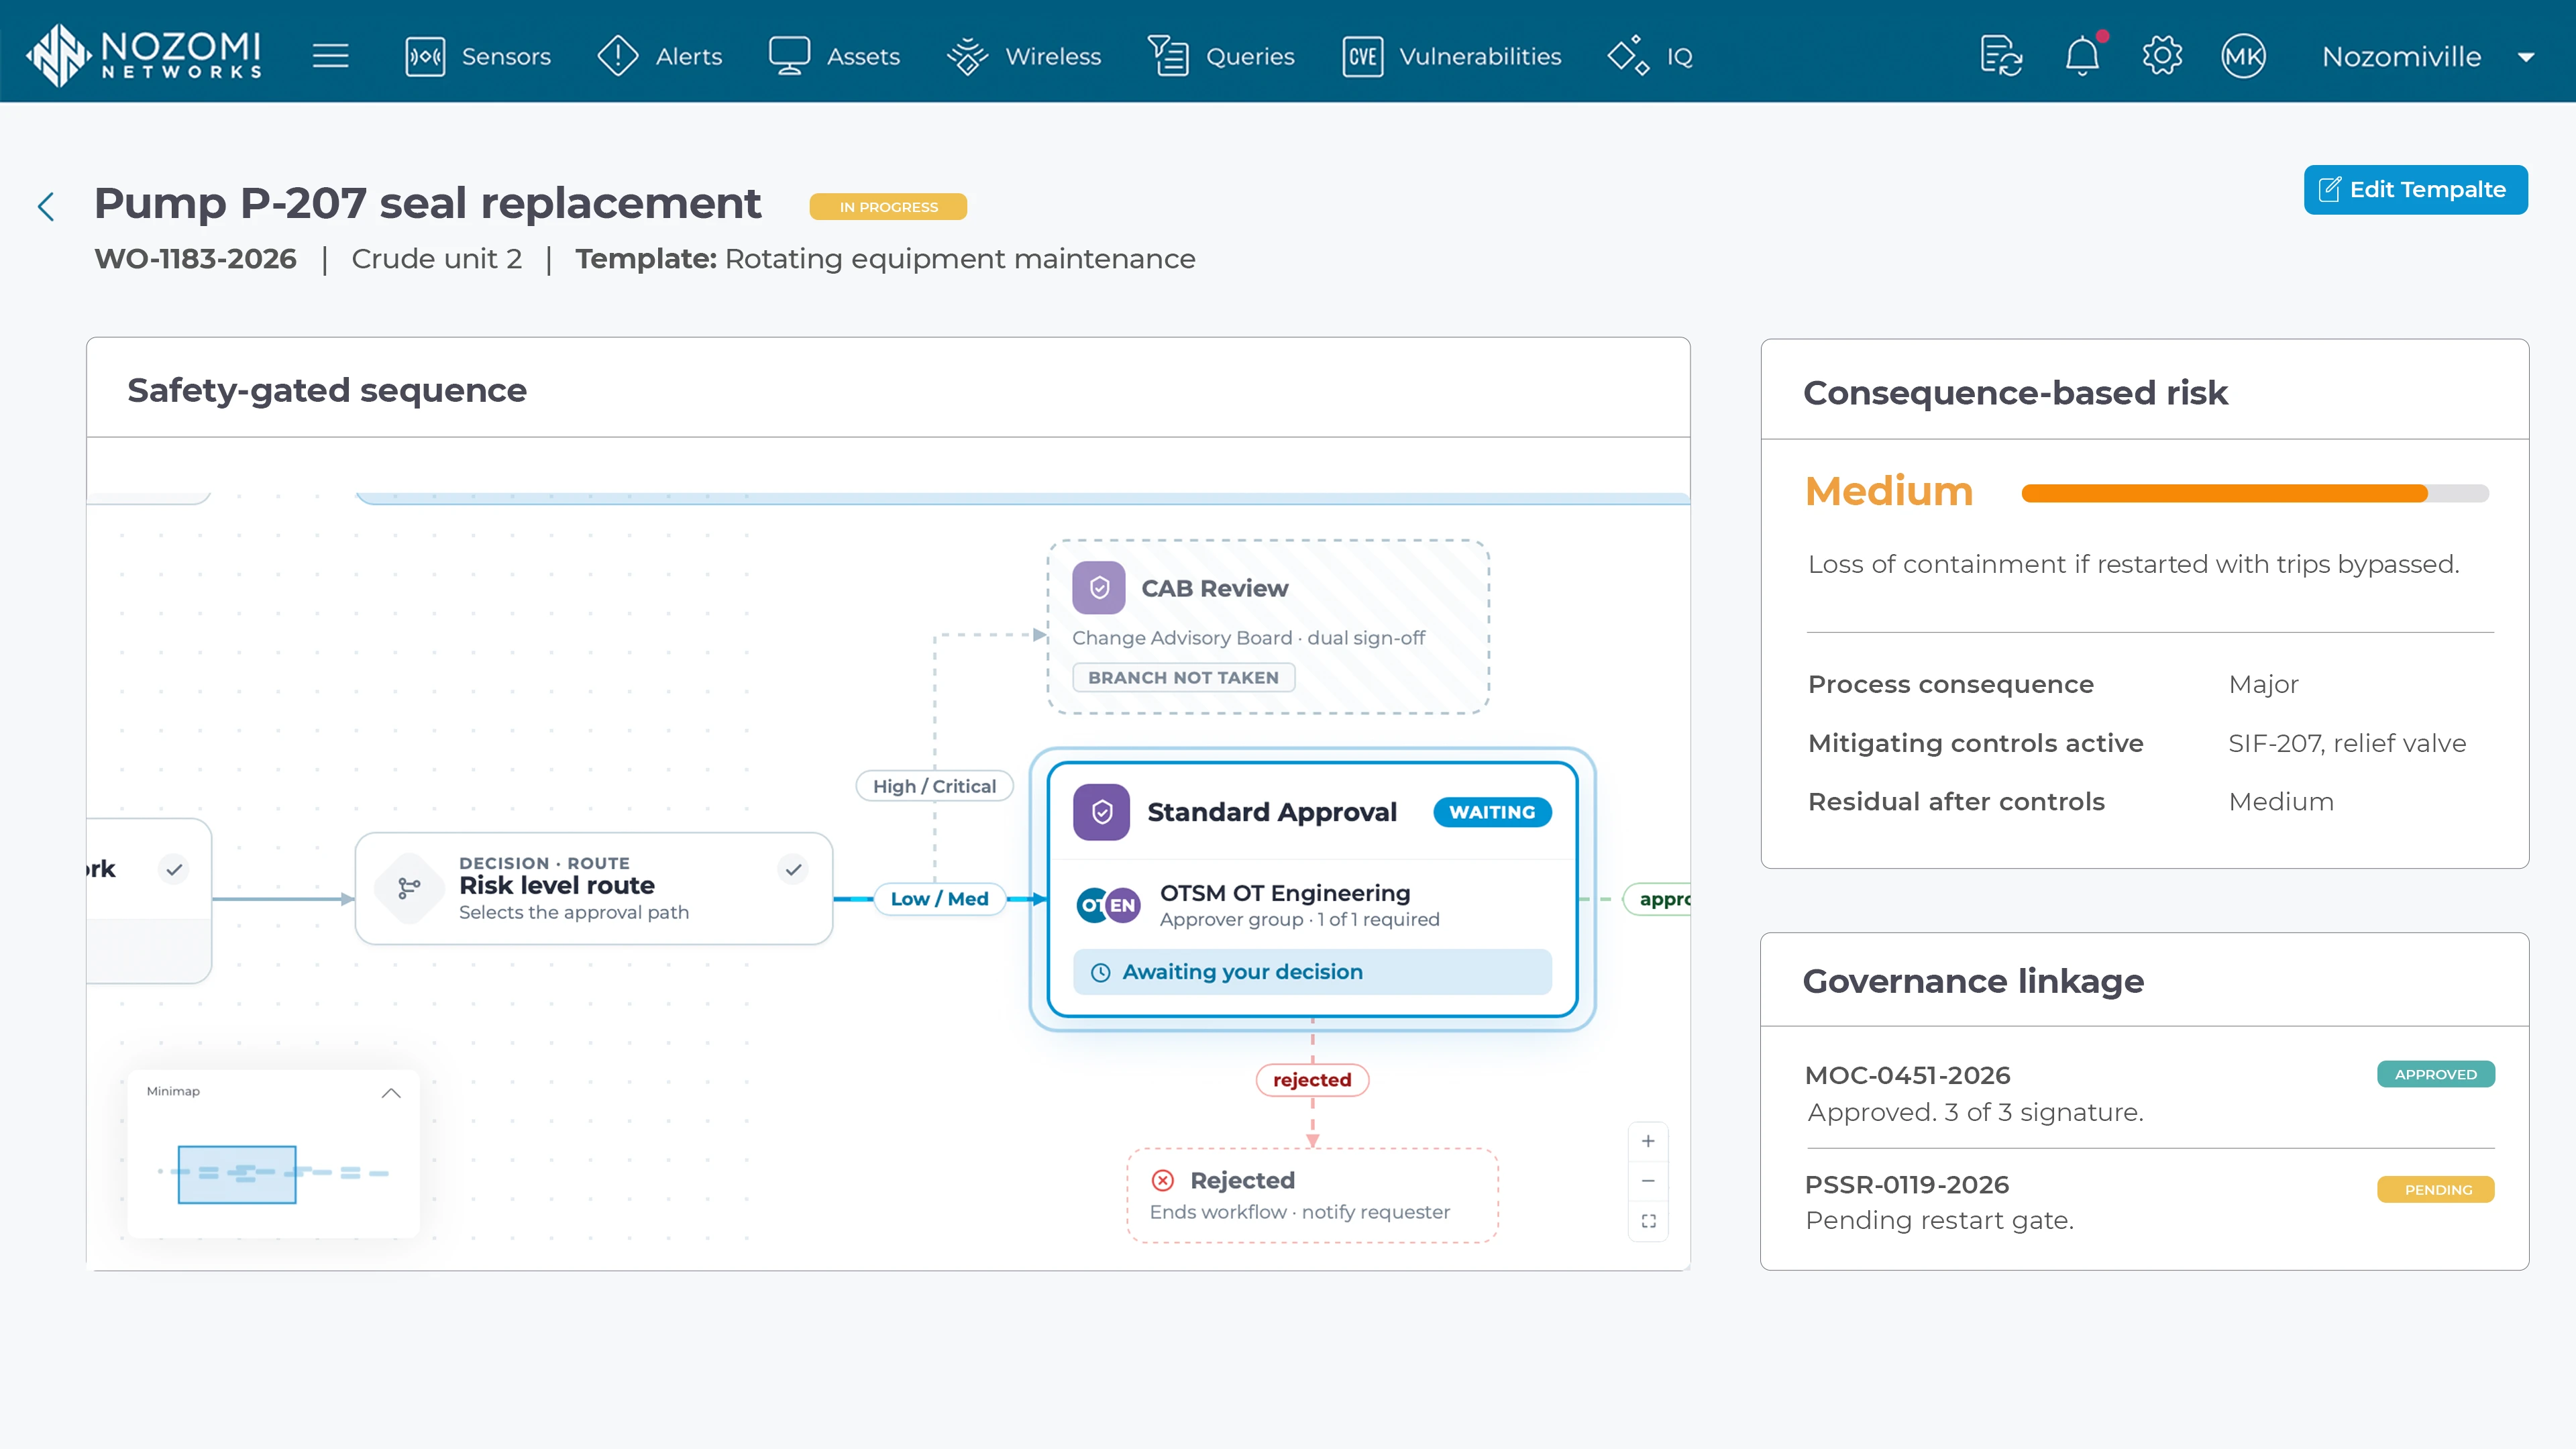
OT-ready and OT-safe, out of the box. OT-specific workflows with process-aware context, safety modeling and Purdue-level asset relationships allow for faster change management and easier governance.
Prevent change management from starting, restarting or being marked resolved until required safety conditions are met.
Prioritize OT risk according to physical-process consequence and the controls already mitigating it, rather than relying only on vulnerability severity scores that don't account for what an asset does.
Connect changes to the Management of Change and Pre-Startup Safety Review processes governing them. Each change closes with a signed, traceable record connecting what was authorized with what was performed.
Start with OT-specific templates and adapt workflows using a no-code designer.
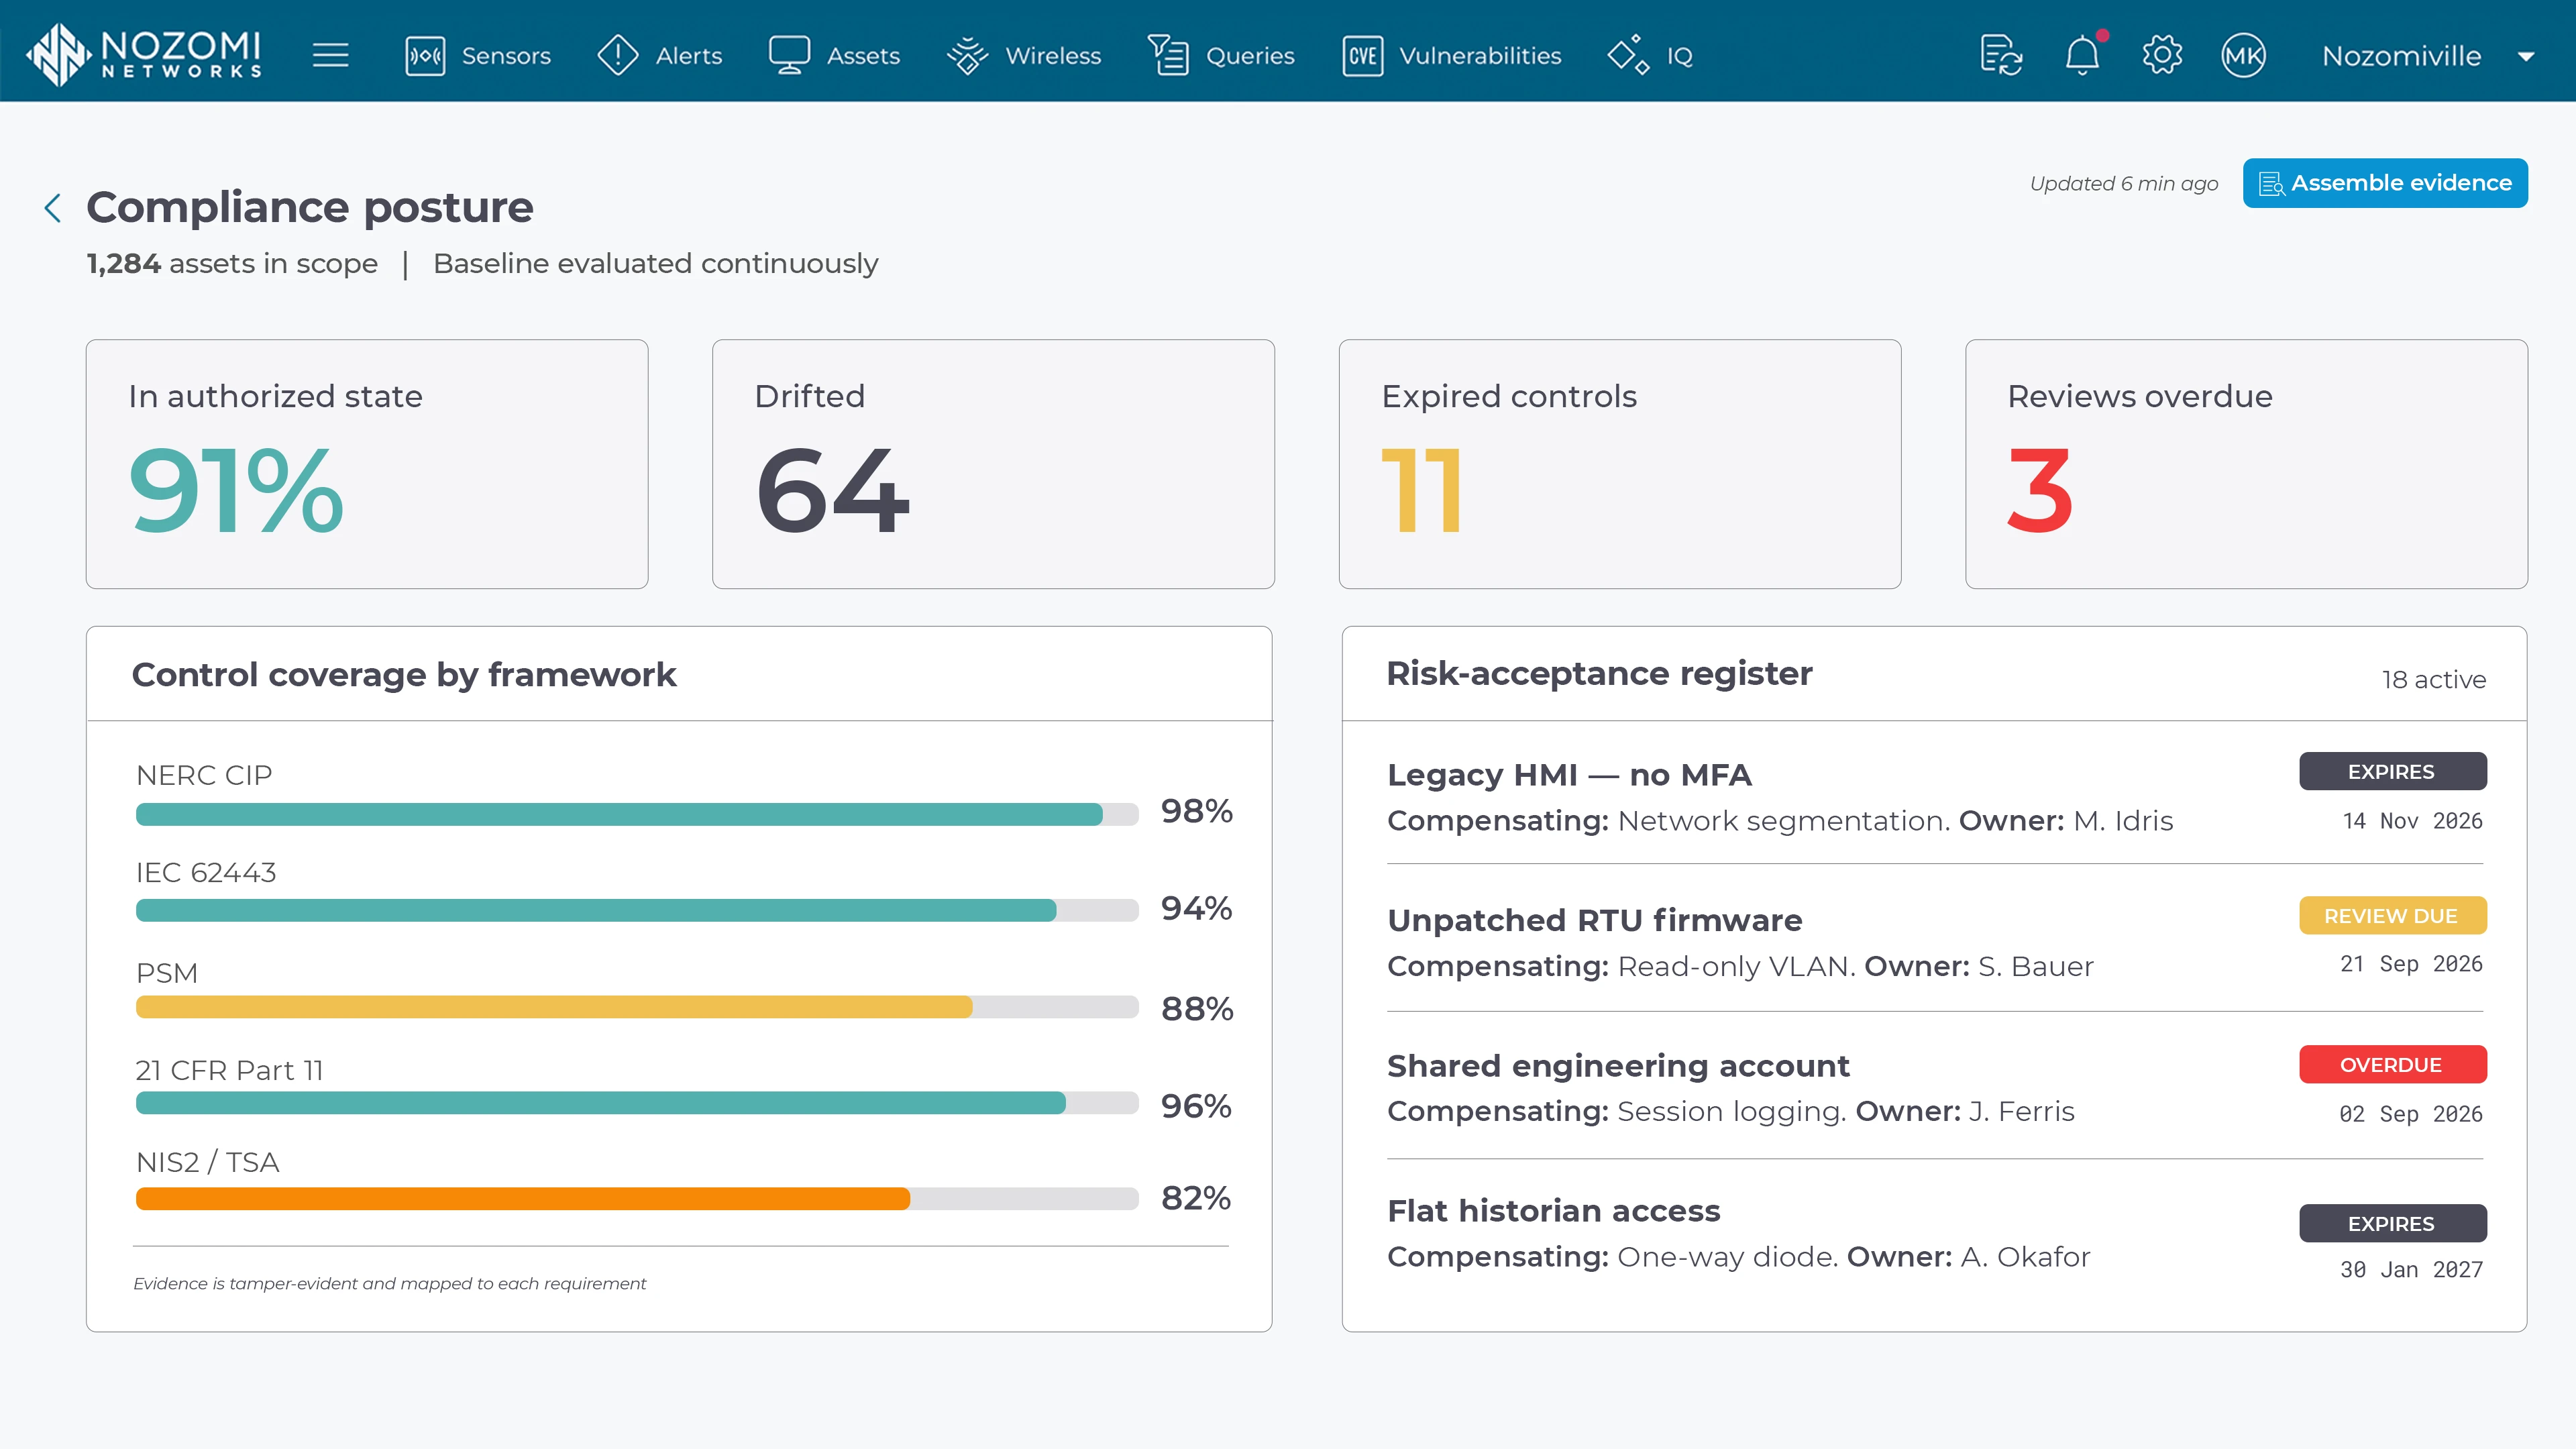
Custom, auto-generated reports provide continuous audit-ready evidence mapped to local and global regulatory frameworks.
Map assets, OT-specific controls and activities directly to regulatory frameworks including NERC CIP, IEC 62443, NIS2, TSA and more.
Generate framework-mapped evidence across assets, controls, changes and time without manual collection.
Track compensating controls, accepted risks, ownership, review cycles and expiration dates. This ensures that exceptions are documented and reassessed rather than silently lapsing.
Identify drift, expired controls and overdue actions before they become audit findings. Compliance becomes an ongoing operational discipline rather than a periodic evidence-collection exercise.