Security configuration assessments (SCAs) are a standard part of cybersecurity programs. Security teams evaluate operating systems, applications, servers and network devices against established security benchmarks to identify misconfigurations, demonstrate compliance and support remediation. In practice, the work is rarely as automated as it should be: results come from several different tools, many checks are still reviewed by hand, and keeping up gets harder with every asset, site and benchmark added.
Today, Nozomi Networks is introducing the first release of a new compliance module in the Nozomi Networks platform, built to automate SCAs and centralize compliance tracking across IT, OT and IoT environments. Unlike existing SCA automation, which was built for enterprise IT, it is designed to assess operational systems safely, including OT environments where today’s tools often can’t be used. The first benchmark it supports is the Defense Information Systems Agency’s Security Technical Implementation Guides (DISA STIGs). It is the first step toward a module that will help organizations assess and demonstrate compliance against a wide range of security frameworks, benchmarks and regulatory requirements.
The capability is being built through a co-development project with Lockheed Martin. Lockheed Martin is providing funding and expertise to support Nozomi Networks, and a team of Nozomi Networks developers in Mendrisio, Switzerland, supported by cyber experts from Lockheed Martin, is building it into the Nozomi Networks platform. That collaboration ties the module’s design to how STIG compliance is performed at enterprise scale in the defense industry.
Why Automated SCAs Are Still Hard to Scale
Mature tools exist for parts of the problem, including endpoint agents, scanners and configuration management systems. The difficulty is applying them consistently to every asset that carries a requirement, and turning the results into evidence an auditor will accept.
- Working out which benchmarks apply to which assets is largely manual. A single system is often subject to several STIGs at once, covering its operating system, the applications it runs and the services it provides, and those assignments have to be maintained as the environment changes.
- Many checks still require manual review, and their results are recorded by hand in separate checklists.
- Environments are distributed across facilities, enclaves and remote locations with limited direct access, and some systems, particularly operational and IoT assets, run continuously and can’t tolerate traditional scanning or be taken offline for assessment.
- Organizations are often left relying on spreadsheets, manual validation and fragmented reporting processes that are hard to maintain and nearly impossible to scale.
At the same time, cybersecurity expectations continue to rise, as risk management frameworks, regulatory requirements and sector-specific guidance increasingly expect organizations to show both that security controls exist and that they remain effective over time. Configuration management is becoming a larger part of that discussion.
DISA STIGs: Growing Pressure to Demonstrate Configuration Compliance
DISA publishes Security Requirements Guides (SRGs) and STIGs published that translate cybersecurity requirements into detailed configuration benchmarks for operating systems, applications, network devices and other technologies. They support implementation of requirements within the DoD Risk Management Framework (RMF) and related cybersecurity programs.
DISA’s guidance states that components “must comply with all SRGs and STIGs applicable to a system,” which “typically results in a system being subject to multiple SRGs and STIGs,” and the requirements extend to systems connected to DoD networks and to systems operated on the DoD’s behalf. They also reach beyond enterprise IT: the DoD Control Systems SRG, first published in 2021 and reissued in February 2026 as the DoD Control Systems/Operational Technology SRG, applies the same approach to industrial control systems and other cyber-physical systems. Today, defense industrial base (DIB) organizations face growing pressure to demonstrate configuration compliance and provide auditable evidence during RMF and authorization activities.
Most organizations still assemble that evidence largely by hand. Existing Security Content Automation Protocol (SCAP) and STIG assessment workflows typically combine the government’s SCAP Compliance Checker for checks that have automated content, DISA’s STIG Viewer to record checks that are reviewed manually, and spreadsheets to track results across systems. That approach works for individual systems but is hard to sustain across thousands of assets, and it is harder still to apply in operational environments containing industrial controllers, engineering workstations and facility systems that may not tolerate traditional assessment techniques.
For many defense organizations, the result is a gap between the requirement to assess and validate security configurations and the tools available to do it efficiently across large environments.
Why Defense Organizations Need Automated SCAs Now
Many defense contractors have moved past the question of whether configuration assessments can be automated and are now asking how to automate them safely and at scale across every environment they operate. Several factors are driving this shift:
- Cybersecurity evidence requirements continue to increase. Security teams are expected to provide repeatable, auditable proof of configuration compliance rather than relying solely on documented policies.
- Programs span enterprise IT, OT and IoT across mission readiness, manufacturing, logistics, facilities management, sustainment and critical infrastructure operations, and all of it falls under the same evidence requirements.
- Defense organizations recognize that manual compliance processes can’t keep pace with the growing number of assets deployed across distributed environments.
Extending STIG Compliance to OT Environments
The Control Systems/OT SRG describes control systems and OT as “prevalent and essential to the function of weapon systems, utilities, facilities, medical systems, manufacturing and the defense industrial base,” and Mission Owners must meet SRG and STIG requirements for all of them. Many of these environments run on Windows and Linux hosts, including engineering workstations, operator stations, historians and operational servers that are subject to the same operating system and application STIGs as any enterprise system.
For OT teams across the government and the DIB, this creates a problem that existing automation hasn’t solved. The tools that automate STIG assessments today were built for enterprise IT. They assume a system can be scanned with administrative credentials, can run additional software, and can be restarted or taken offline if something goes wrong, none of which can be taken for granted in OT. The same SRG notes that “many control system/OT processes are continuous in nature,” that “unexpected outages of systems that control industrial processes are not acceptable,” and that outages “often must be planned and scheduled days or weeks in advance.” Its guidance is to use OT-specific vulnerability scanning tools and techniques only “where safe and feasible.”
A 2017 audit by NASA’s Office of Inspector General shows what happens when those assumptions don’t hold. It found that “applying traditional IT security practices to OT systems can cause the underlying systems to malfunction.” In one case, vulnerability scanning caused equipment to fail and cut communication with an Earth science spacecraft during an orbital pass. In another, a security patch intended for standard IT systems triggered a reboot that stopped an engineering oven’s control software, resulting in a fire that destroyed spacecraft hardware inside the oven.
As a result, even where automated STIG tools are available, OT teams often can’t use them, for reasons like these:
- Credentialed network scans and IT-oriented agents generally haven’t been validated against operational systems, and running them can put availability at risk.
- Systems can’t be rebooted or taken offline outside planned maintenance windows.
- Sites are often remote and segmented from enterprise networks, with limited direct access to host-level configuration data.
- Without a safe automated option, compliance for these assets is assessed by hand through spreadsheets and checklists, and in some cases not at all.
Introducing the Nozomi Networks Compliance Module
Nozomi Networks has spent more than a decade securing OT and IoT environments, and the compliance module is built with these constraints in mind. Using Nozomi Arc sensors, organizations can safely collect the host-level configuration data needed to evaluate endpoints across IT and OT environments against DISA STIG benchmarks, without relying on traditional IT-centric assessment approaches. Arc collects configuration evidence directly from the host without credentialed network scans, operating primarily in user space and using kernel-level modules only when necessary, mainly in read-only mode. Passive monitoring of network communications adds asset context without sending traffic to sensitive devices. OT assets are assessed against the same benchmarks and policies as IT assets, and their results appear in the same asset profiles, managed centrally across distributed sites from the Central Management Console (CMC) on premises or in the cloud using using Vantage or Vantage for Government, our FedRAMP® Class C (Moderate) SaaS platform. For assets where an endpoint sensor can’t be deployed, the safe active polling planned for future releases is intended to extend coverage while respecting OT operating constraints.
For government and DIB organizations, that means STIG compliance can be demonstrated from one platform across IT, OT and IoT, including the operational systems that are frequently still assessed by hand.
This approach enables security teams to:
- Automate configuration assessments across distributed IT, OT and IoT environments
- Centralize compliance visibility across assets, policies and benchmarks
- Track assessment posture and changes over time
- Review pass/fail findings and associated evidence
- Investigate individual rule-level findings and remediation guidance
- Integrate configuration assessment activities into broader security and compliance workflows
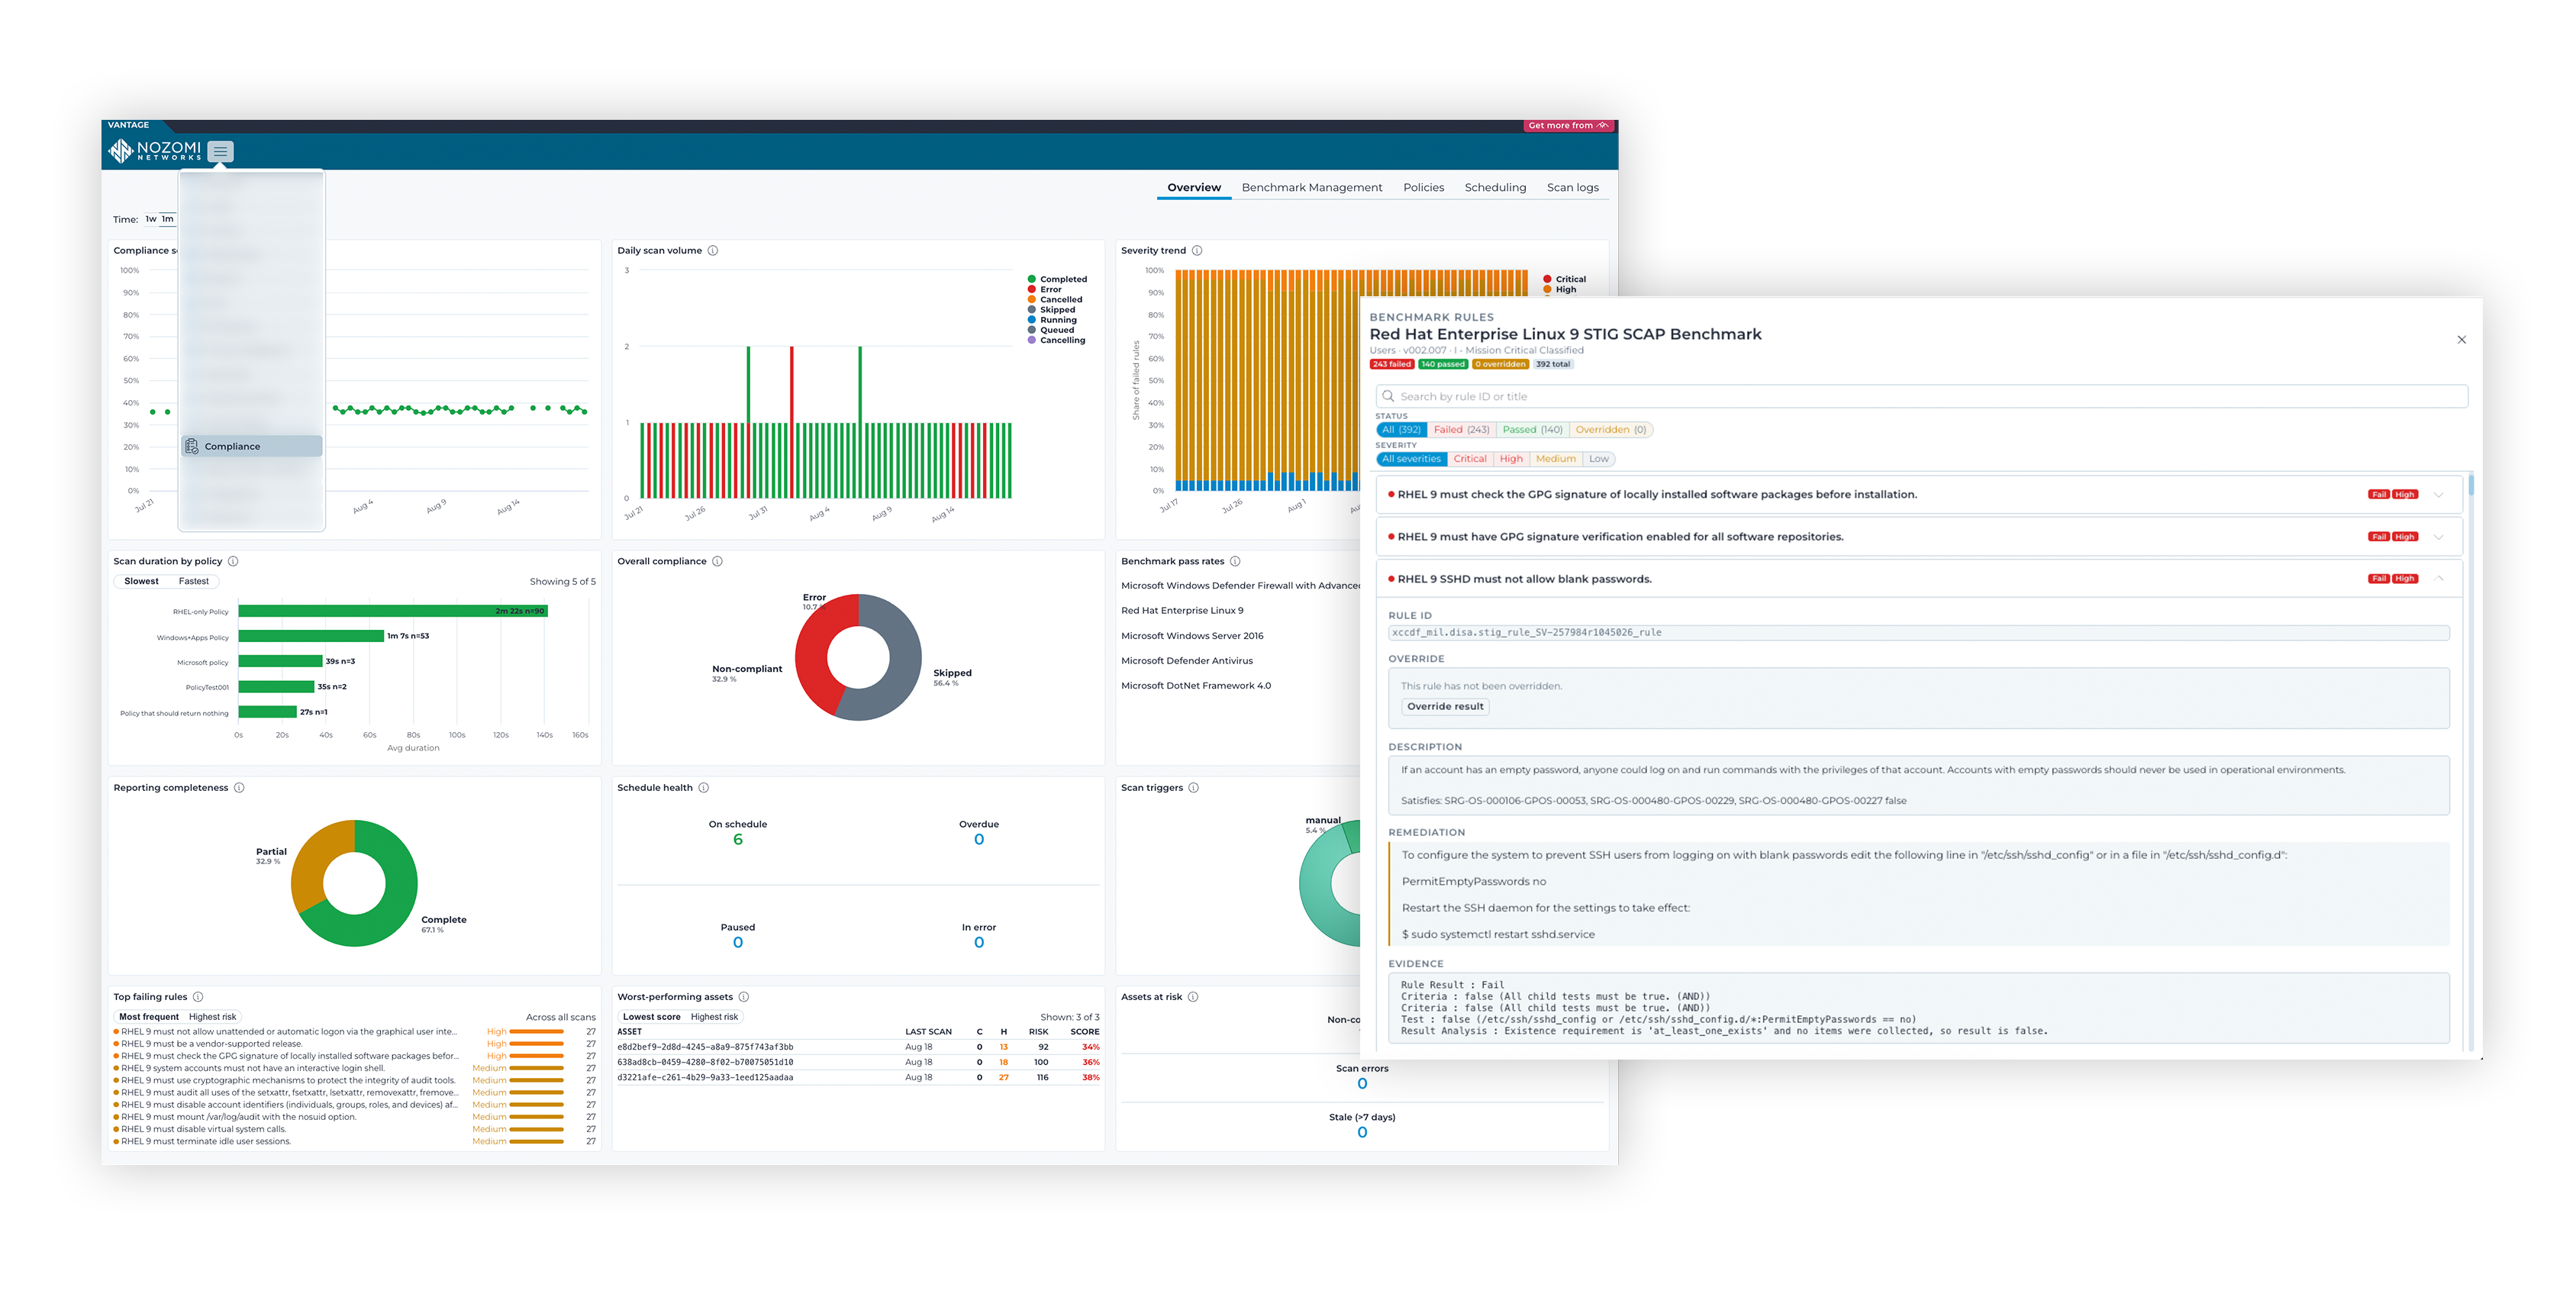
Unlike traditional compliance approaches that depend on multiple tools, spreadsheets and disconnected reports, the platform provides a centralized view of configuration posture across IT and operational environments. Organizations can quickly understand which assets are compliant, which benchmarks are failing, where risk exists and what actions should be prioritized. It also places configuration assessment results alongside asset inventory, vulnerability data, risk information and other operational security context, so teams can use compliance results to decide which risks to address first.
DISA STIGs Are Only the Beginning
Organizations increasingly need efficient ways to evaluate configurations, collect evidence and demonstrate compliance across diverse IT, OT and IoT environments. DISA STIGs are the first benchmark type the compliance module supports, and development with Lockheed Martin continues. Upcoming releases are planned to automatically identify the STIGs that apply to each asset, including those tied to the services an asset provides, such as directory, DNS or web services, so teams no longer have to work out and maintain those assignments by hand. We also plan to extend the module to additional security frameworks, benchmarks and regulatory requirements. The goal is a compliance module that lets organizations map and evaluate their own security requirements against every asset they operate.
If there’s a security configuration framework, benchmark or regulatory requirement you would like to see supported next, please contact us today.